Blog

  • WWDCS CEO On Operational AI In Border Security 

    WWDCS CEO On Operational AI In Border Security 

    WWDCS CEO On Operational AI In Border Security

    Operational AI for the Physical World was at the heart of conversations at AI Reality Summit 2026 in San Francisco this year.  WWDCS was there in the room alongside more than 200 senior leaders from security, public safety, critical infrastructure, and smart cities. The discussion focused on what operational AI means for border and critical infrastructure security. 

    Across two days, Dave Harmon, CEO of WWDCS, engaged in discussions with senior leaders, technology innovators and operational specialists. One challenge that came up repeatedly during the sessions: the gap between what AI can do and what organisations can realistically deploy. The conversation also focused on addressing the challenges of sustaining AI in live operational environments. 

    Taking to the main stage, Dave delivered a presentation, “From Situational Awareness to Orchestrated Actions Across Contested Borders“ built on WWDCS’s expertise in delivering integrated security programmes across border and critical infrastructure environments.

    His session addressed the defining challenges of modern border operations; sensors, cameras, vehicle and vessel movements, personnel reports and intelligence feeds, spread across agencies that rarely share a single picture. 

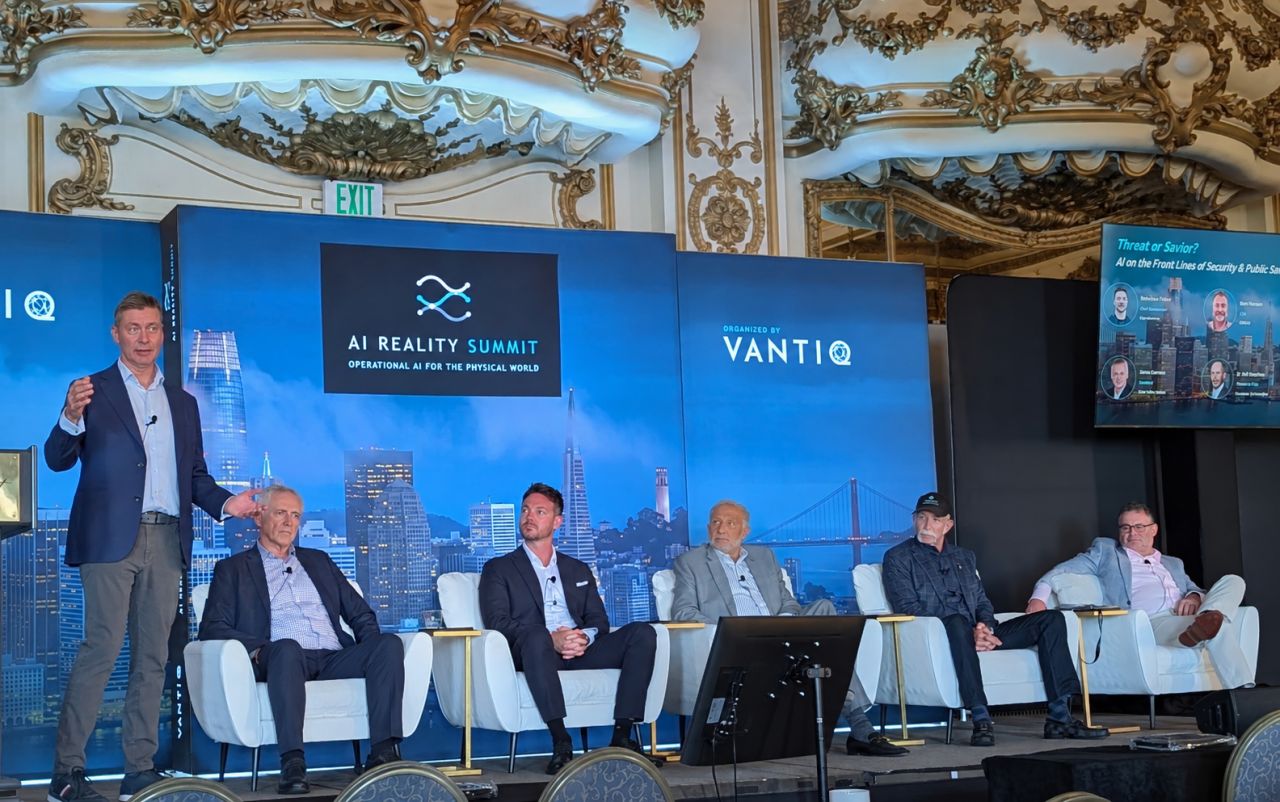
    Dave also joined a panel discussion on “Threat or Savior? AI on the Front Lines of Security and Public Safety,” alongside senior leaders from OpenHorizon, Safe Cities Global, Goodman Technologies and Ironwave Technologies, moderated by Vantiq’s Global Head of Defence. The panel explored the urgent questions facing security and public safety organisations in a post-AI world. 

    The Summit provided an opportunity to examine how operational AI is being applied across security environments. It also focused on the implications for their design, command, and operation. 

    Summarising his thoughts on the topic and the summit, Dave said

    “The future of border security will not be defined by how much intelligence we collect, but by how effectively we act on it. In complex operational environments, information is often fragmented across systems, agencies, and jurisdictions. At WWDCS, our focus is on bridging these gaps, bringing together technology, intelligence and operational expertise to enable faster, more coordinated responses. AI presents an opportunity to take this further, moving beyond situational awareness to meaningful action on the ground.”
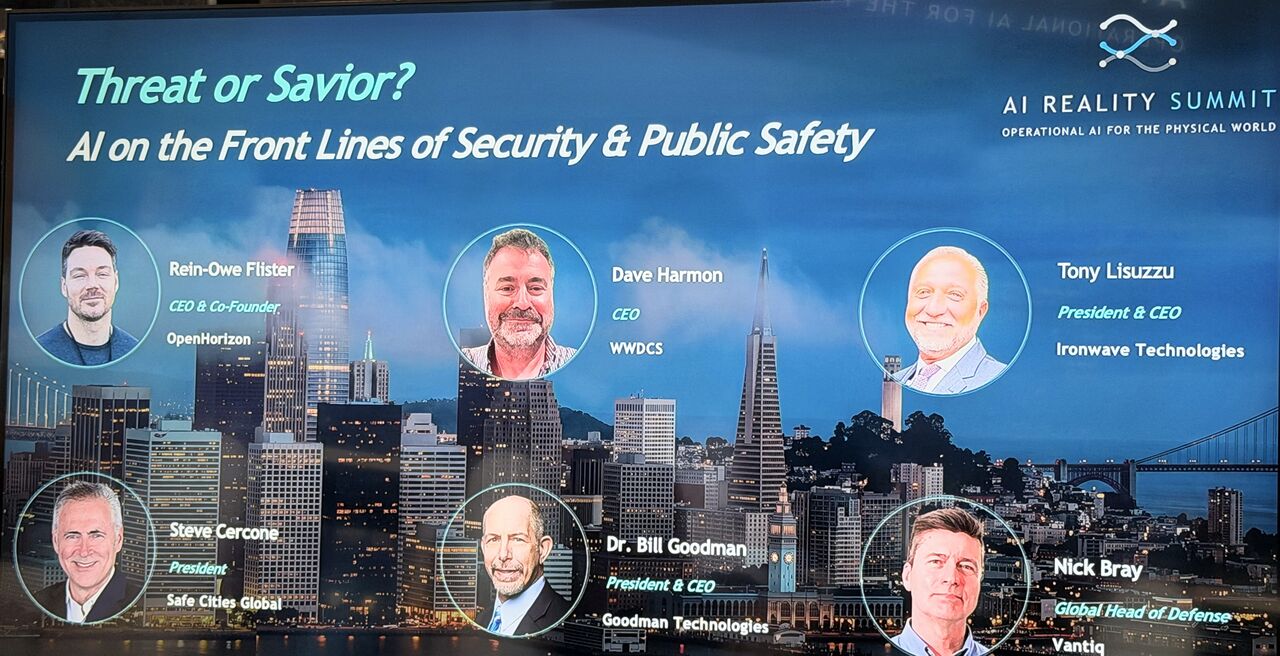
    WWDCS was pleased to be part of the event and thanks Vantiq for convening a timely and thought-provoking conversation around operational AI and its role in real-world environments. 

    About WWDCS 

    WWDCS is a bespoke security solutions provider with over a decade of experience delivering integrated security programmes for organisations operating in high‑risk environments, working across government, borders security, critical infrastructure, and commercial sectors. 
  • Inside the International Border Management & Technologies Association (IBMATA) Europe Summit 2026: WWDCS on the Future of Border Security 

    Inside the International Border Management & Technologies Association (IBMATA) Europe Summit 2026: WWDCS on the Future of Border Security 

    Inside the International Border Management & Technologies Association (IBMATA) Europe Summit 2026: WWDCS on the Future of Border Security

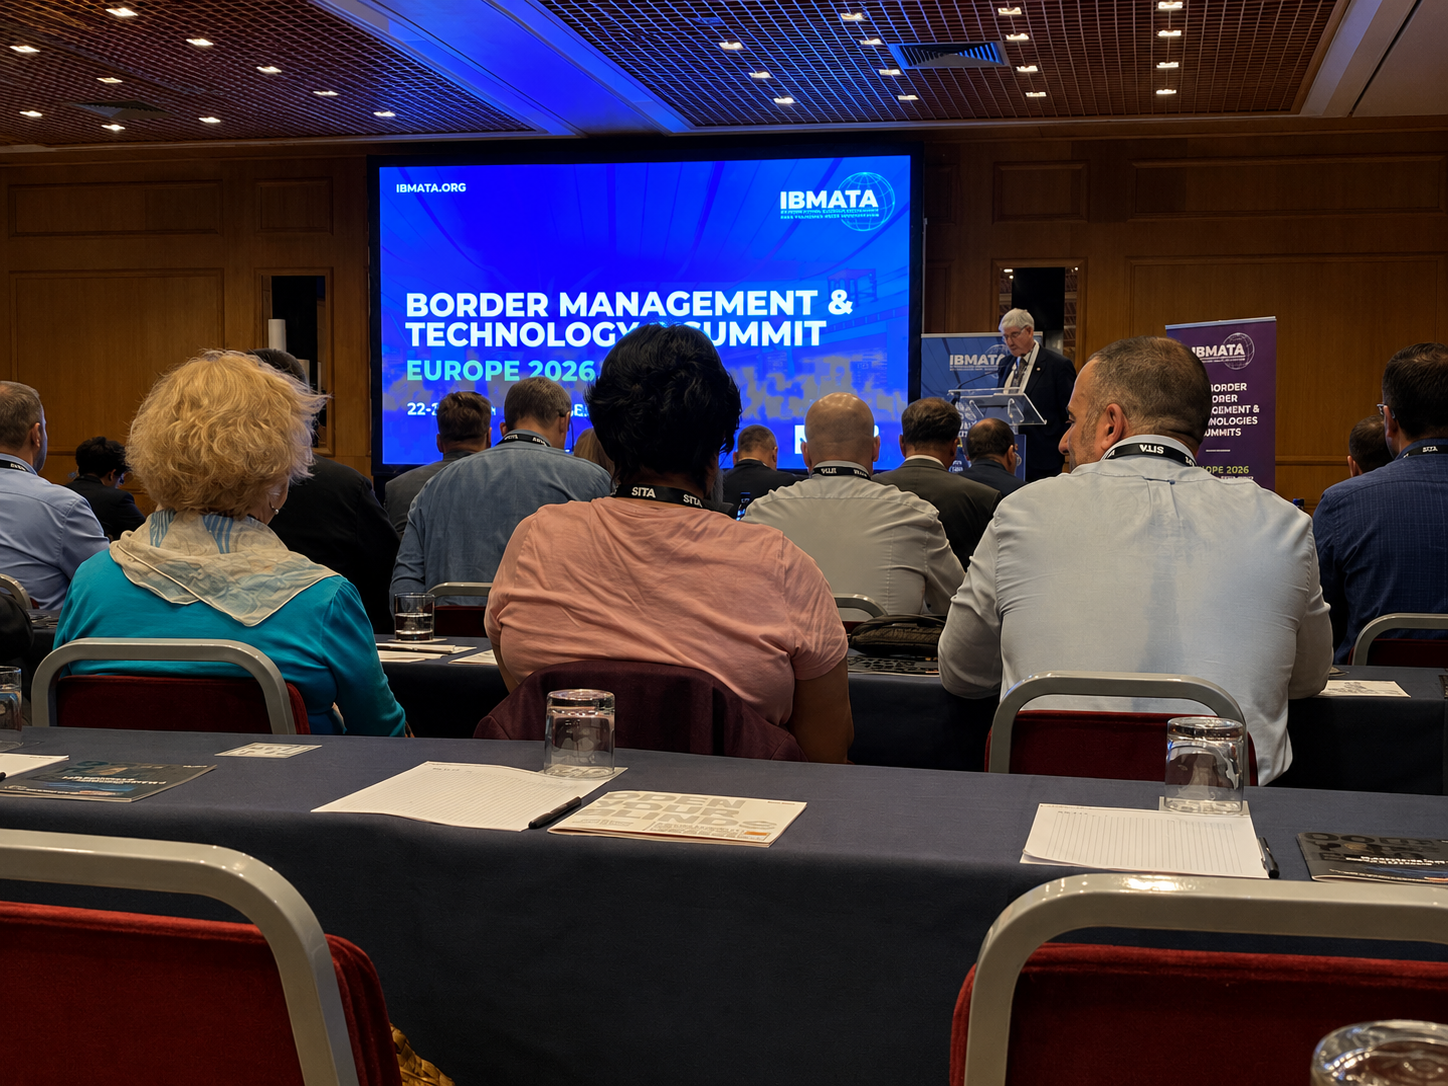
    What does it take to shift border security from reacting to threats to anticipating them? That question sat at the centre of this year’s International Border Management & Technologies Association (IBMATA) Europe Summit, held 22–24 June in Lisbon – and WWDCS was there to help answer it. 

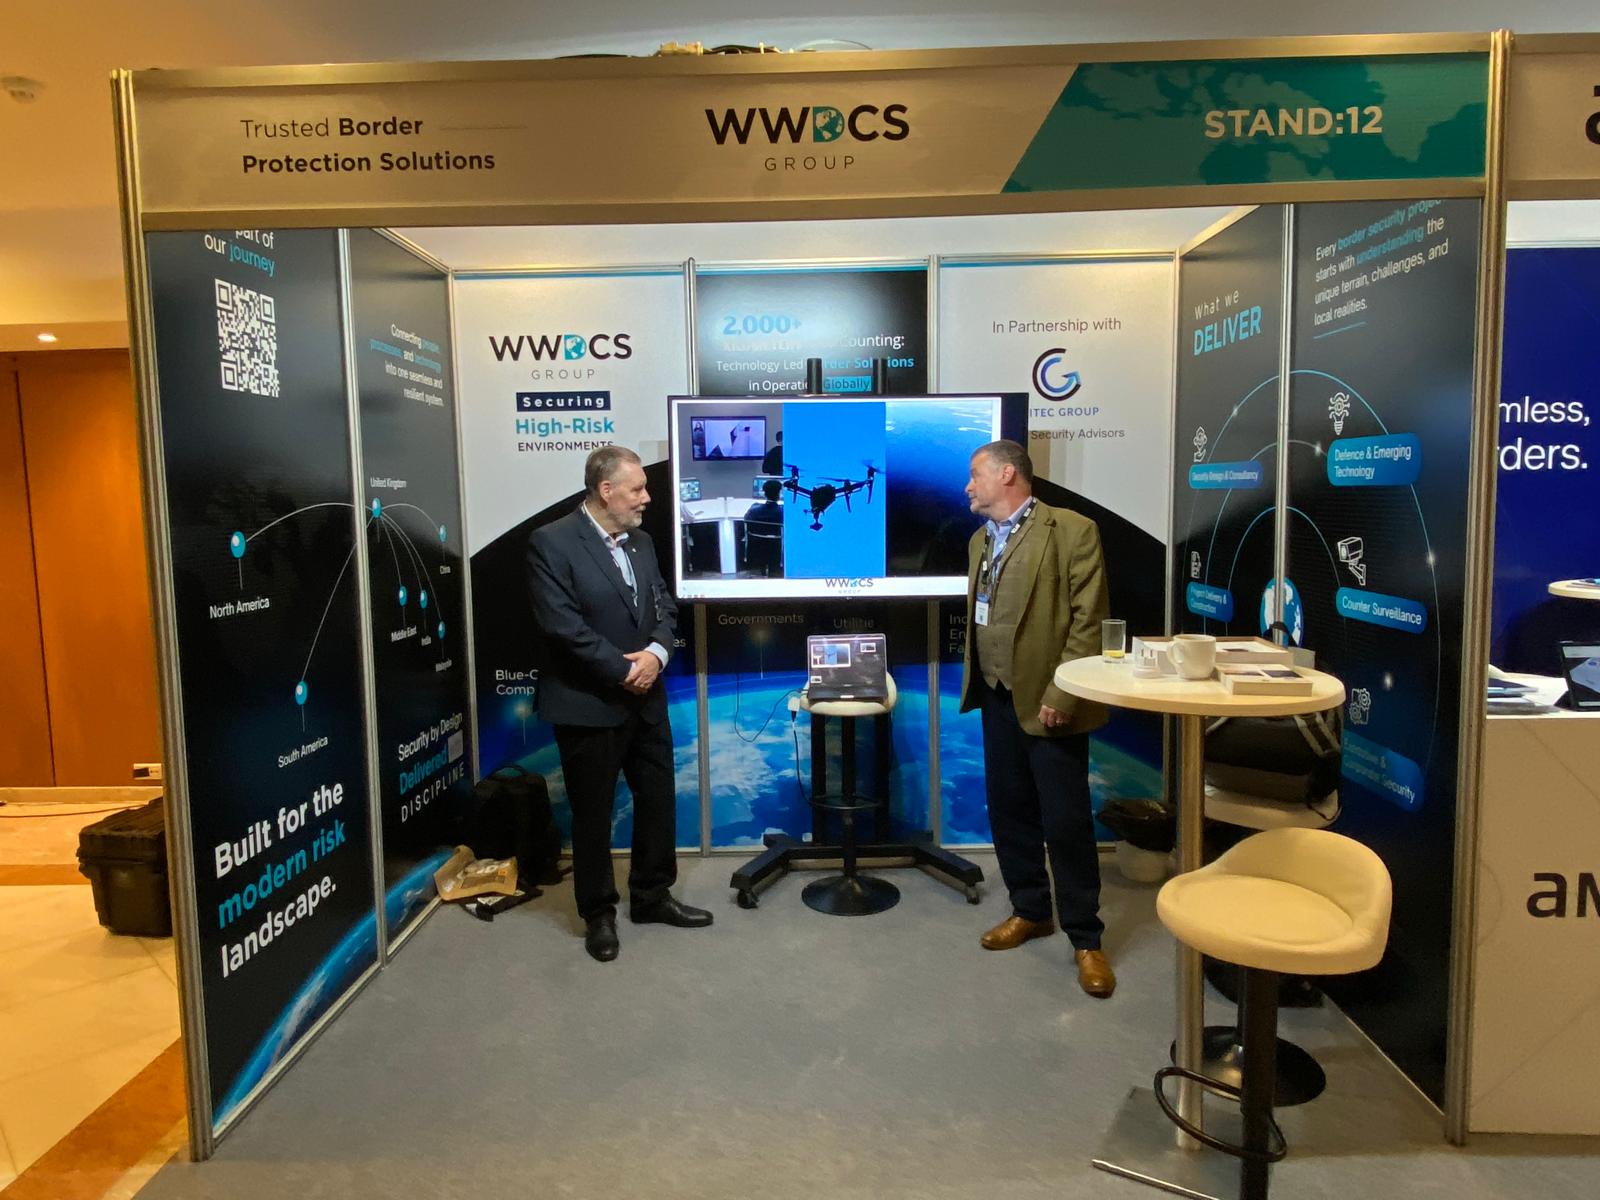
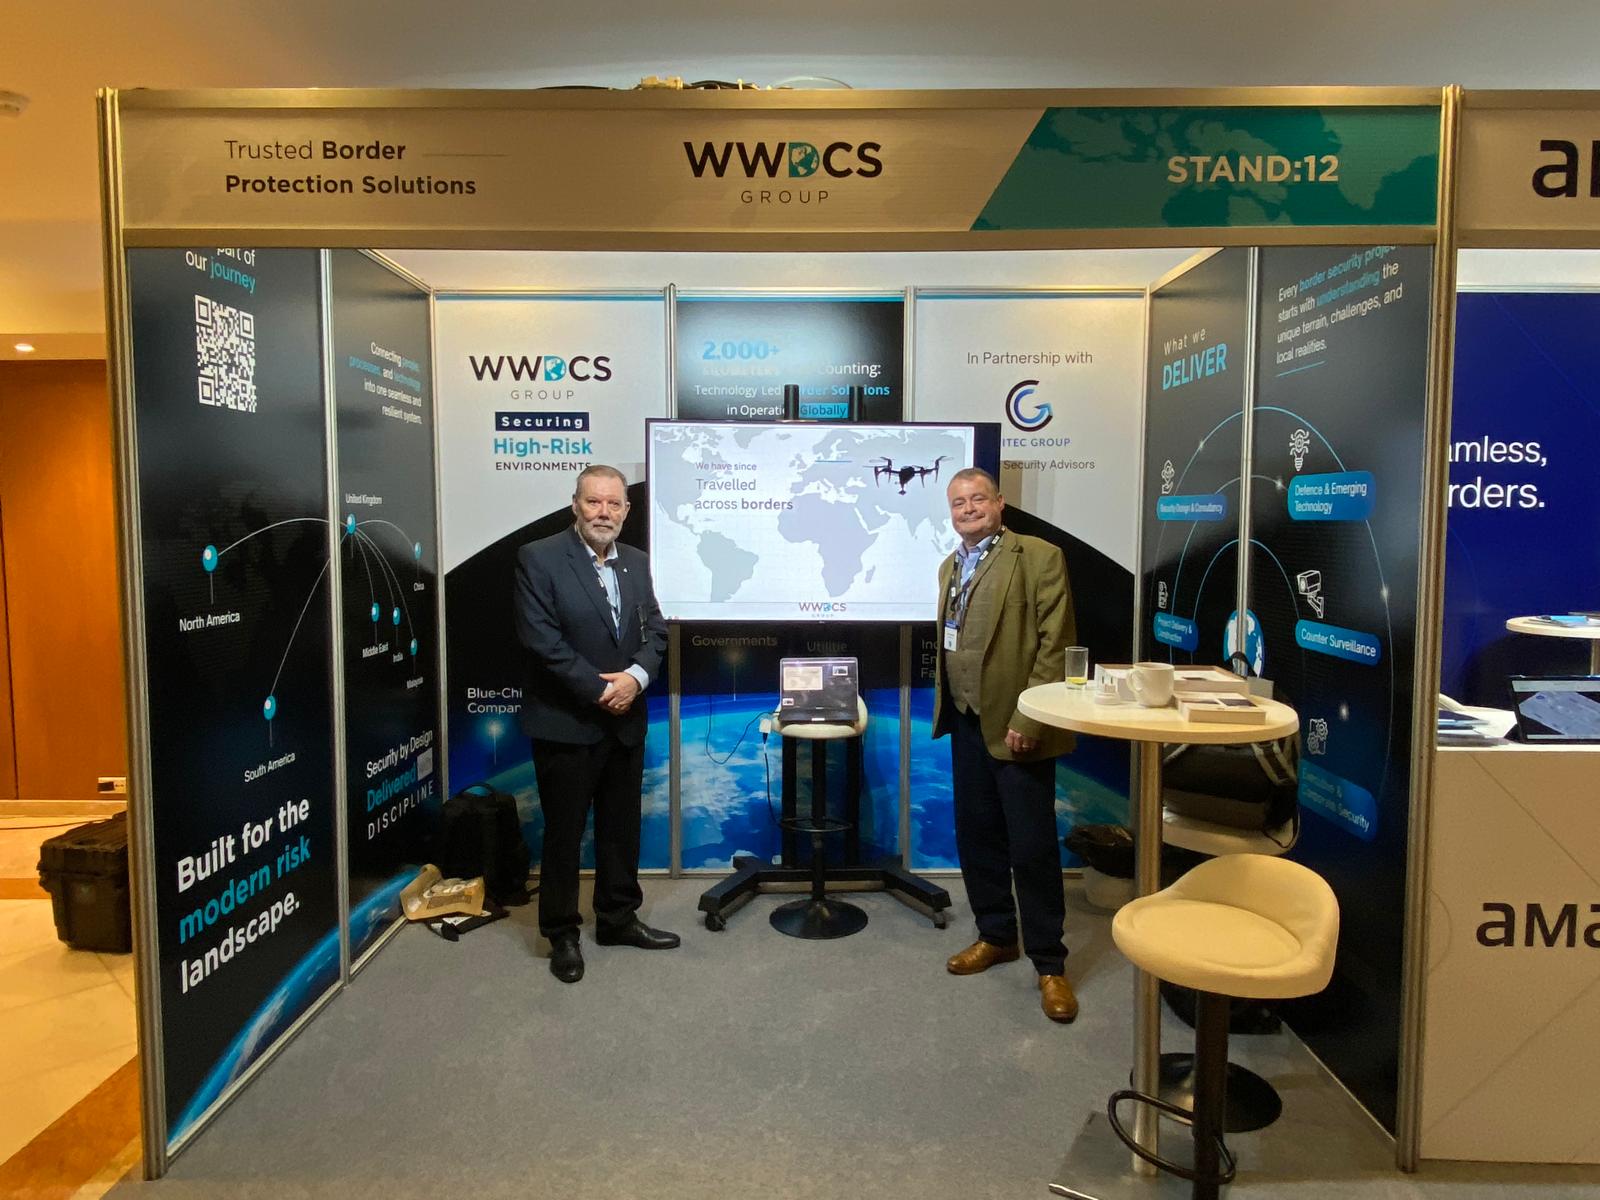
    WWDCS sponsored and exhibited at the Summit, represented by Chairman Frank Doherty and Director Dave Harmon, engaging across three days of discussion with senior government officials, border agencies, and security leaders from across Europe. Conversations repeatedly returned to the same pressure points: migration management, cross‑border crime, and the accelerating move toward intelligence‑led operations. 

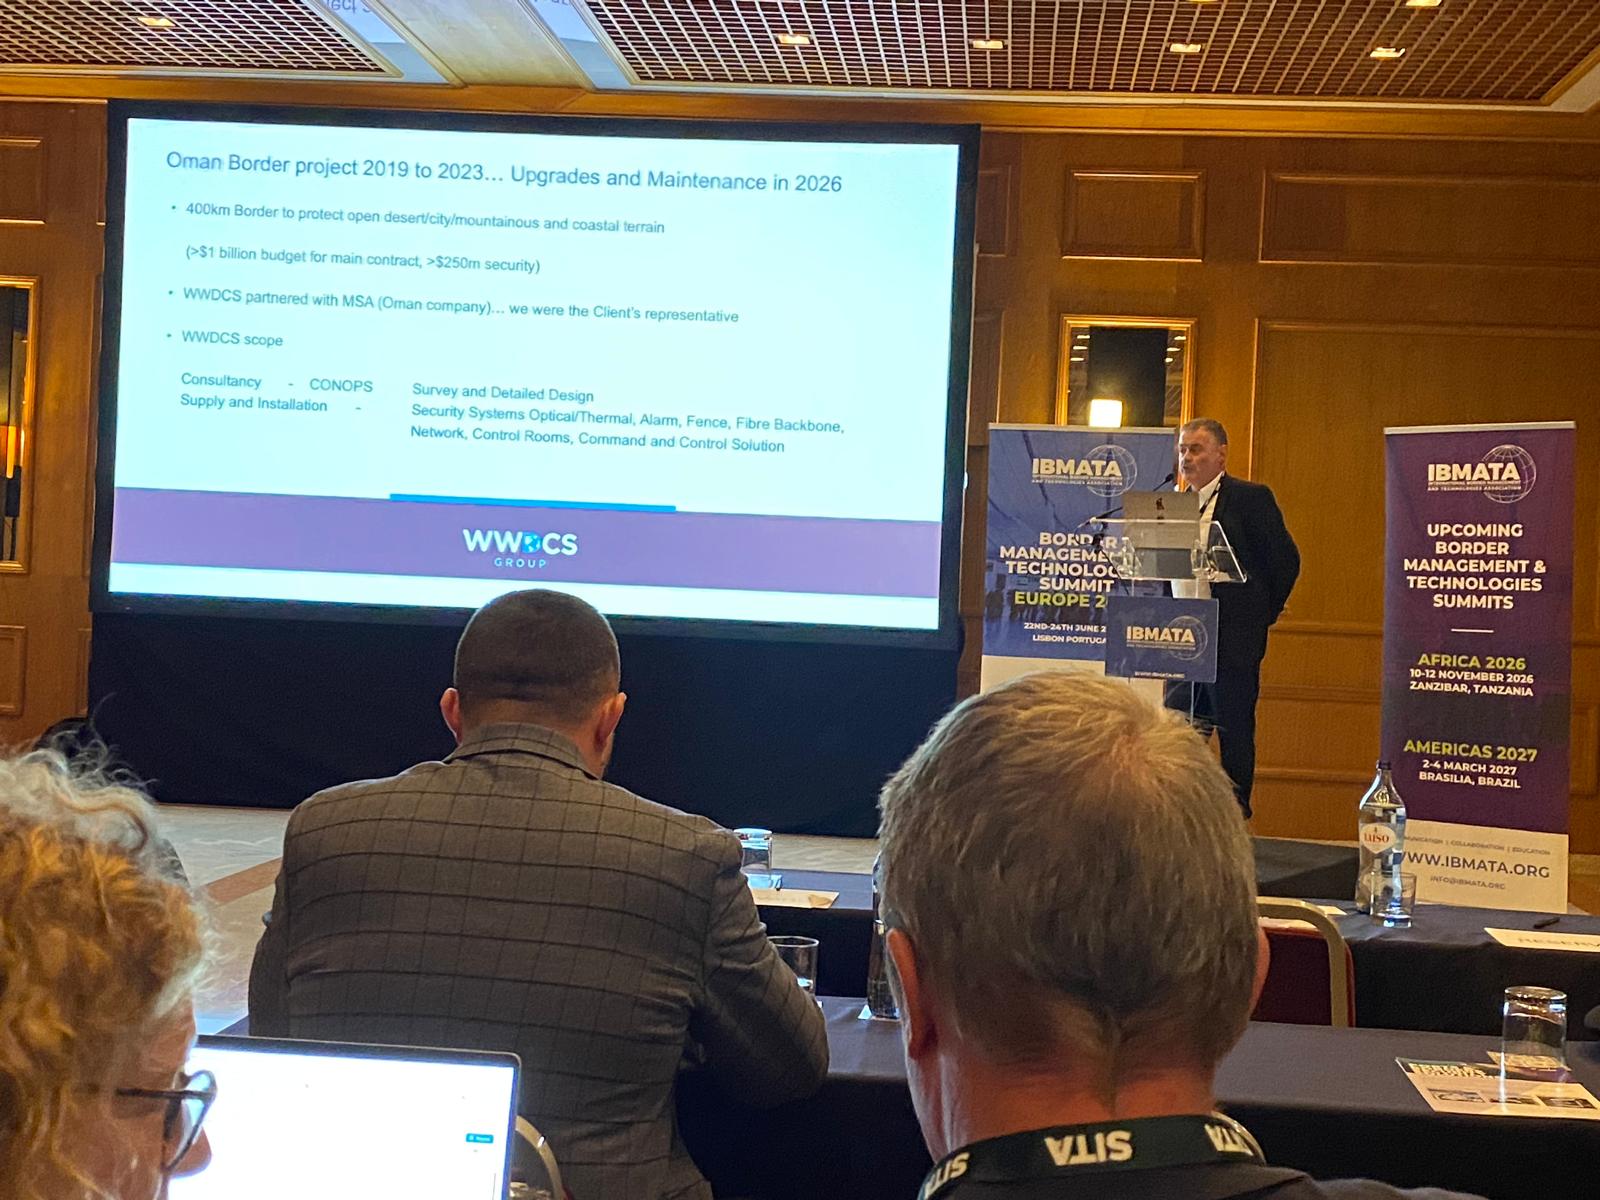
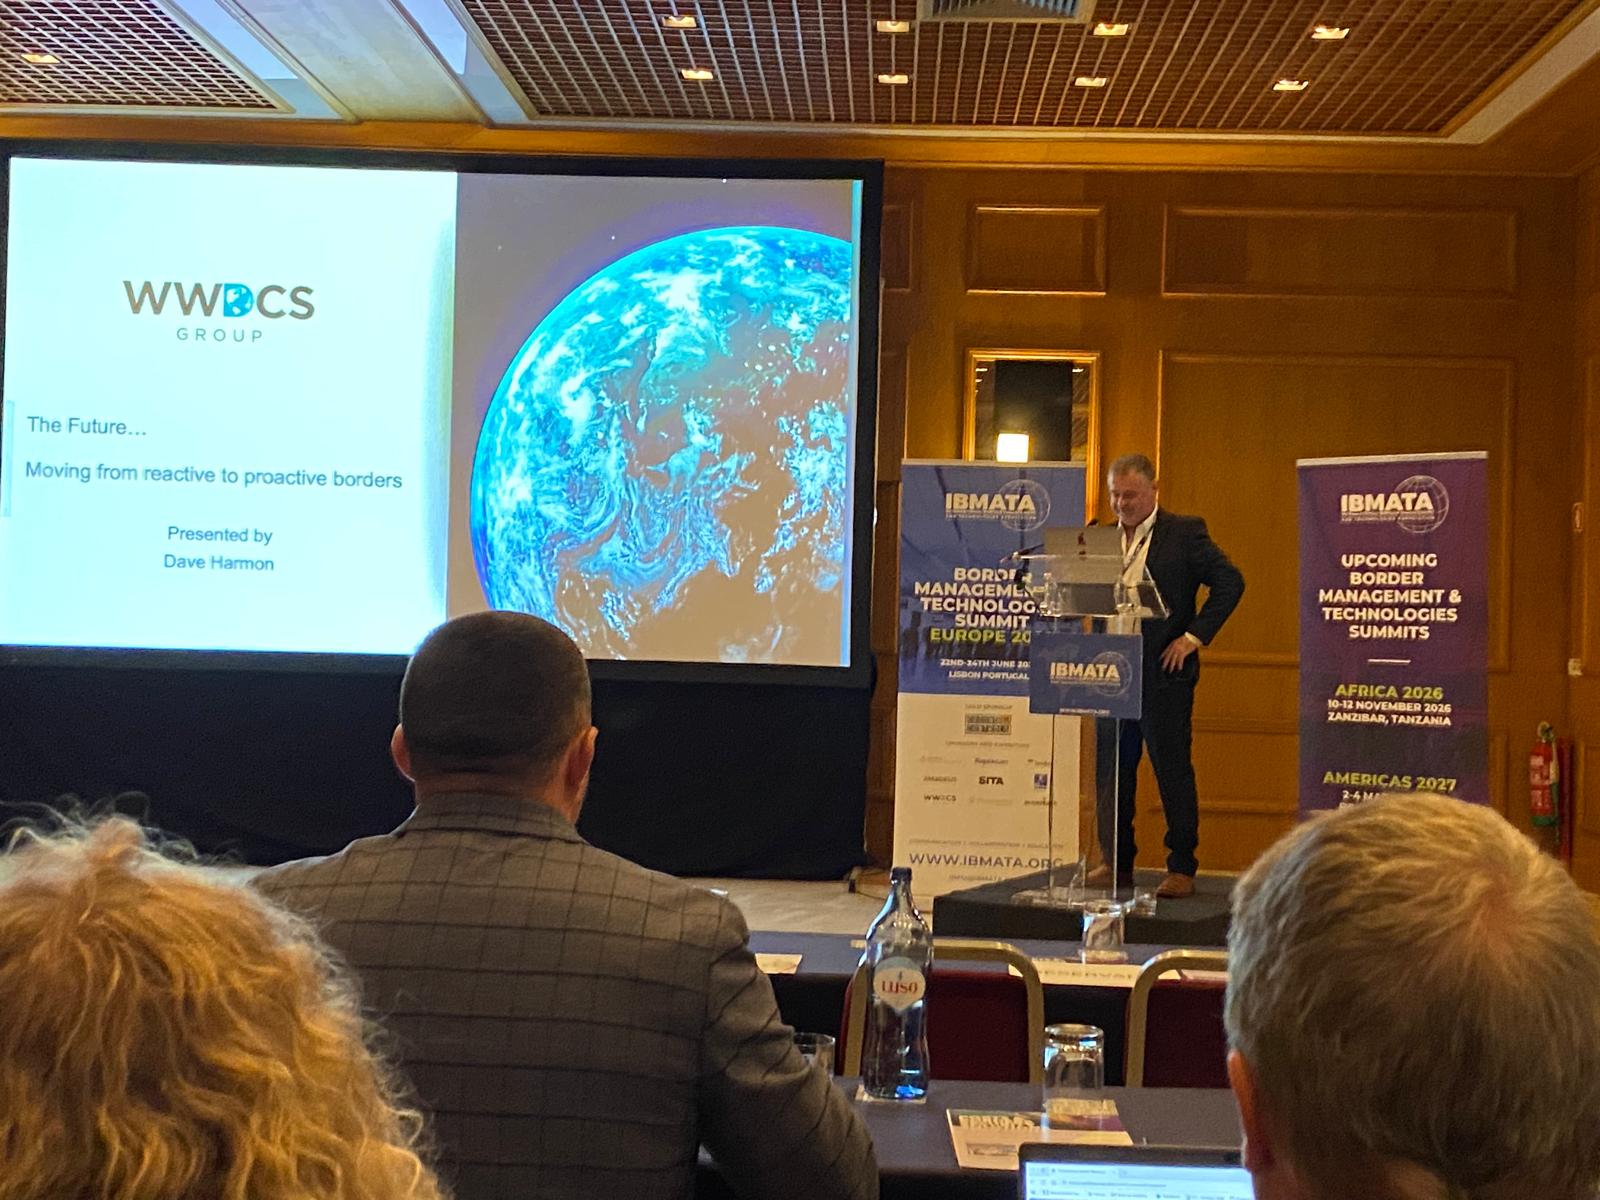
    Dave delivered a featured presentation, “The Future: Moving from Reactive to Proactive Borders,” drawing on WWDCS’ experience delivering integrated security solutions in complex, high‑consequence environments. His session explored one of the Summit’s most prominent themes: the widening gap between acquiring new technology and embedding it into day‑to‑day operational practice – and what closing that gap truly demands from agencies and their partners. 

    WWDCS attended alongside partner Critec Group, represented by CEO Mark Hobday and Operations Director Andy Thompson, continuing a collaboration focused on delivering practical, integrated security solutions to the border management sector. 

    If there was one takeaway from the IBMATA Europe Summit 2026, it is that technology alone does not solve border security challenges. People, process, and integration do – and that is where WWDCS places its focus. 

    WWDCS was proud to participate in this year’s Summit and extends its thanks to the IBMATA team for hosting a successful and forward‑looking event. 

    About WWDCS: 

    WWDCS is a bespoke security solutions provider with over a decade of experience delivering integrated security programmes for organisations operating in high‑risk environments, working across government, critical infrastructure, and commercial sectors. 
    The Summit was also covered by Border management summit | Professional Security Magazine

  • Supply Chain Security: The Blind Spot Boards Can No Longer Ignore

    Supply Chain Security: The Blind Spot Boards Can No Longer Ignore

    Supply Chain Security: The Blind Spot Boards Can No Longer Ignore

    A board approves a new tier-2 supplier with contracts signed and compliance boxes ticked. Eight months later, an operational breach occurred. Not through their own facility, but through a connected partner. The investigation reveals the vulnerability had existed for months, visible to anyone looking, invisible to everyone responsible. In 2026, this is not an assumption. It has become a pattern. 

    What This Means for Boards

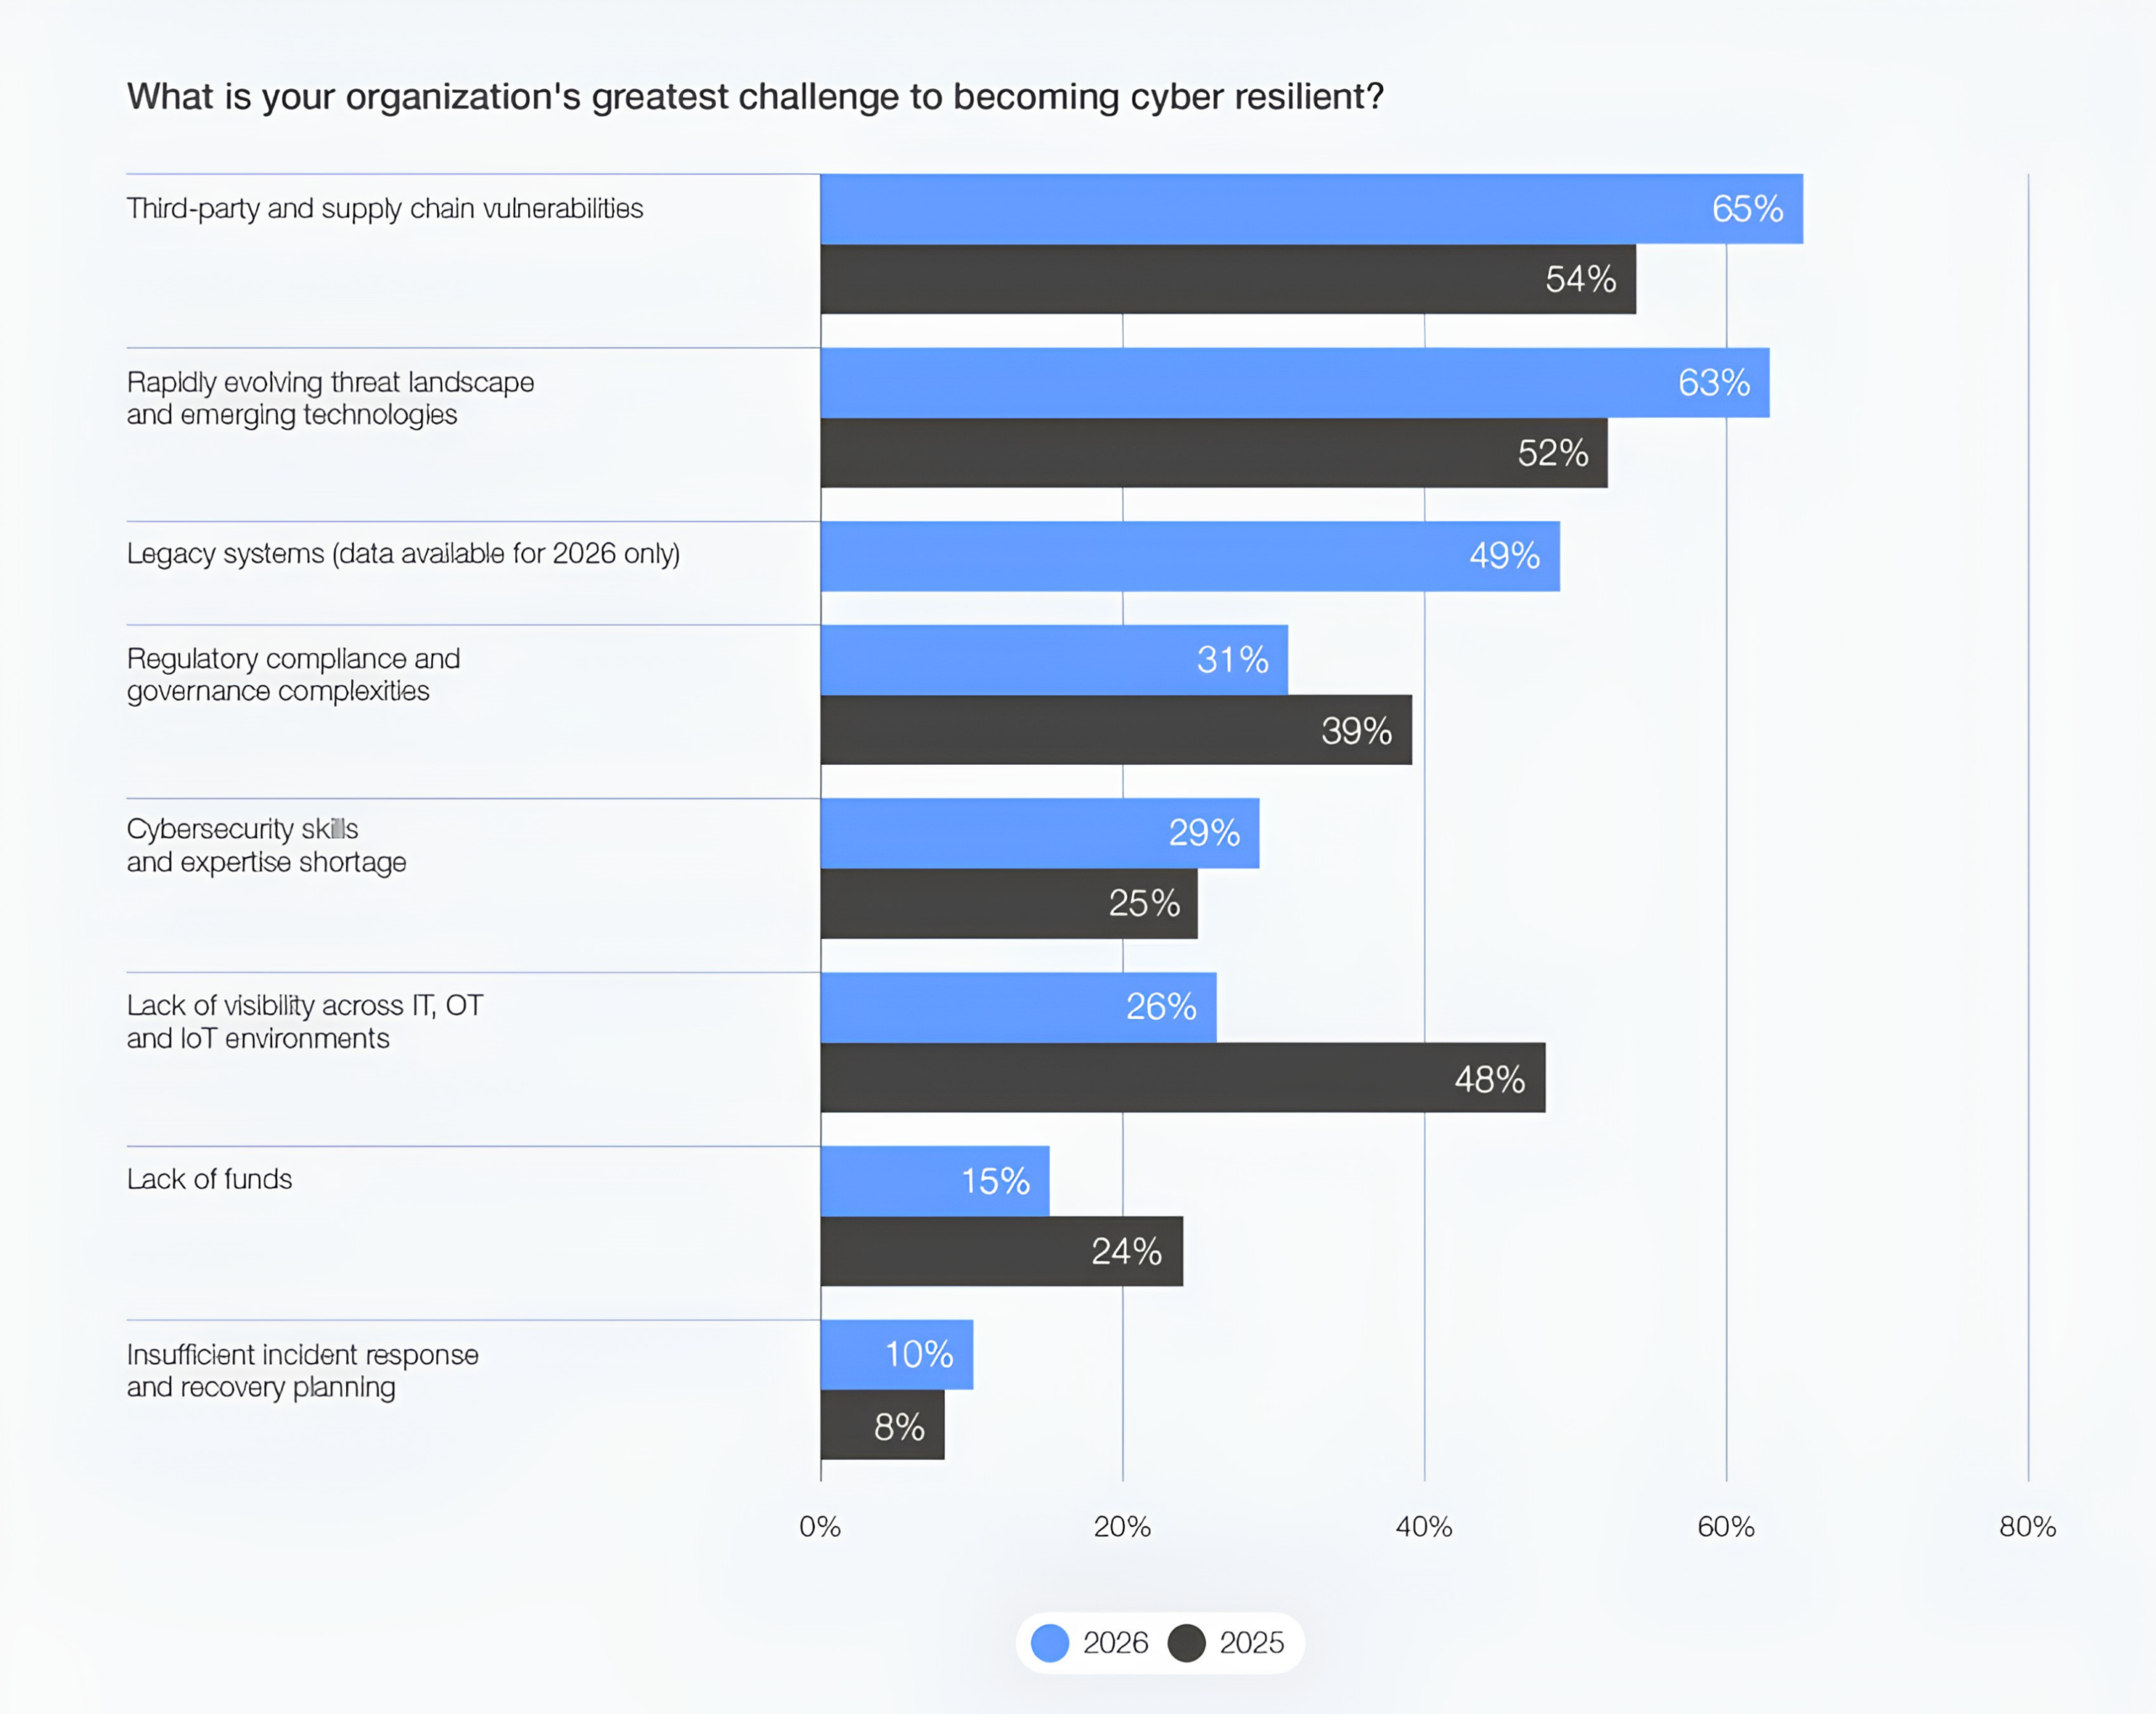
    The World Economic Forum’s (WEF) 2026 report highlights third-party and supply-chain vulnerabilities as a major challenge to organisational resilience. Yet many organisations still lack a clear picture of their wider supplier networks, making it difficult to assess how a disruption at one supplier could affect operations elsewhere.

    Many organisations still have limited visibility beyond their immediate suppliers, making it difficult to identify emerging risks before they become operational problems. The perimeter extends beyond an organisation’s own premises to include supplier sites and contractor facilities.

    Resource: World Economic Forum

    Why The Blind Spot Persists

    The problem is not awareness. Most organisations recognise the vulnerability, yet 78% admit their internal security programmes cover less than 50% of their total vendor ecosystem. Why does this gap persist? 

    Three structural failures keep it open.

    • First, a visibility gap: only 41% of organisations monitor risk beyond their direct suppliers. Tier-2 and Tier-3 partners operate almost entirely unseen.  
    • Second, an accountability gap: security responsibility diffuses across procurement, legal, and operations, with no single function truly owning supplier risk.  
    • Third, and most critically, an assumption gap: ISO certifications, SOC 2 reports, and supplier security questionnaires create the appearance of diligence without reducing risk. Compliance frameworks are minimum baselines and not security guarantees.     

    In practice, a supplier may meet contractual requirements while weaknesses remain in site access controls, and incident reporting. Unless these arrangements are assessed beyond the immediate supplier, gaps may only become apparent when an incident disrupts operations.

    The 2026 Shift: Governance and Resilience

    The regulatory landscape has strengthened the role of senior leadership in supply chain security. Under NIS2 and DORA, management bodies have defined responsibilities for overseeing cybersecurity and digital operational resilience, including the approval and supervision of relevant risk-management measures.  

    In the US, SEC disclosure requirements also place greater emphasis on board oversight of material cybersecurity risks. Together, these developments reinforce the importance of effective governance, clear accountability, and ongoing risk management across the supply chain. 

    The question boards are now being asked by regulators, investors, and insurers is:

    Can you demonstrate that your security posture extends across your entire operational ecosystem?  

    For most organisations, the honest answer remains no.  

    What End-To-End Security Actually Looks Like

    Most organisations now recognise that supply chain security is not just a procurement issue. It has a direct impact on business continuity, resilience, and reputation. 

    In practice, this means four things working together. First, tiered supplier risk classification, so security architecture must reflect actual exposure levels. Second, physical and operational assessments beyond digital audits including site access controls, personnel vetting, and facility vulnerability reviews at contractor and partner locations. Third, integrated incident response protocols that extend beyond an organisation’s own perimeter, and fourth, real-time visibility through live monitoring platforms that help identify emerging threats across connected environments.

    The Value of Cross-Environment Experience

    Organisations facing supply chain challenges often assume that their risks are unique. Many sectors face similar problems. Lessons learned in critical infrastructure, logistics, border security, and industrial environments can often be applied elsewhere. The key is understanding where dependencies exist and where disruption is most likely to occur. 

    A weakness in contractor access controls, gaps in supplier oversight or unclear incident response procedures can create risks across different environments. Understanding how these issues emerge, and how they affect operational continuity, helps organisations identify vulnerabilities earlier and take practical steps to reduce the likelihood and impact of disruption.

    The Question Every Board Must Now Answer

    Supply chain security is no longer simply a procurement, operational, or cyber issue. It is a business resilience issue that requires Board-level attention. Organisations that understand their dependencies, look beyond their immediate suppliers, and maintain visibility across their wider operating environment will be far better placed to prevent disruption and respond effectively when incidents occur. 

  • Drones Over the Fence: Why Autonomous Aerial Threats Are Rewriting Physical Security Playbooks

    Drones Over the Fence: Why Autonomous Aerial Threats Are Rewriting Physical Security Playbooks

    Drones Over the Fence: Why Aerial Threats Are Rewriting Physical Security

    For decades, physical security strategies have been built around fences, gates, cameras and access controls. The assumption was that threats would approach from the ground. Drones have fundamentally changed that assumption.

    Drones, also known as Unmanned Aircraft Systems (UAS), have emerged as a rapidly evolving security threat across critical infrastructure, industrial facilities and high-security sites. Ministry of Defence, reports that in 2025 UK, reports that in 2025 alone, there were more than 250 drone incidents near military areas. Drone strikes near airports increased by more than 25% in the first quarter of 2025, as compared to 2024. As a result of this, airspace infractions are now considered as operational threats by security personnel.  

    There is an increase in the risk exposure for power plants, substations, prisons and aviation centres. Drones are becoming an attractive tool for the criminal groups as they can be used for both surveillance and target physical attacks. Every security leader now, must answer this question: 

    Is current security architecture capable of identifying, evaluating and reacting to the growing aerial threats? 

    Where Do Traditional Security Systems Fall Short?

    With the increase in the security breach incidents, organisations have made significant investment in ‘Perimeter Security’ including ground-based monitoring systems, CCTV and access control, all of which are considered as the part of traditional security framework. Since these were created to fight for two-dimensional security threats, they still are crucial precautions. Majority of the current security frameworks were not designed to fight the third-dimension attacks in which the drones operate.

    A drone does not need to pass through a gate, breach a fence or defeat a perimeter alarm to gain access to a protected site. While staying completely out of sight from ground-based monitoring systems, it can survey map and deliver a payload. Legal frameworks regarding this new threat are still in development phase, a new restriction on unmanned aircraft came into effect from January 2026. When threats are present and increasing rapidly, the organisations cannot afford to wait for the regulations to direct the response.  

    What Does an Integrated Counter Drone System Look Like?

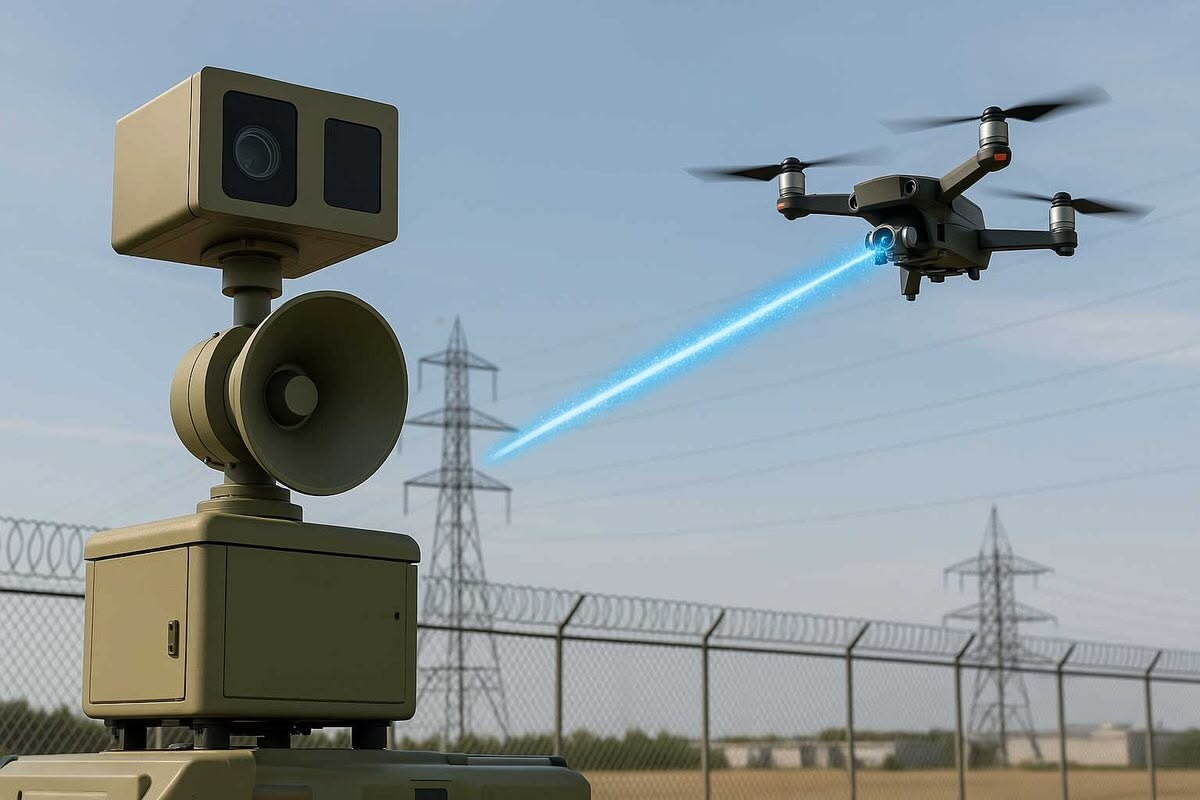
    An effective counter-drone system begins with detection. Radar, radio frequency (RF) sensors and visual analytics can identify drones operating in or near a protected area. Each detection must then be assessed in real time to distinguish authorised activity from potential threats and determine the appropriate response. 

    Over the next 10 years the global counter-drone market is predicted to expand with 30% annual growth rate, reaching $30.5 billion by 2034. This is a clear signal of the scale of investment this threat demands across every sector. 

    The Control Room: The Critical Link in the Response Chain

    Many existing control rooms were not designed to act on airspace intelligence. Detection system alone is insufficient if alerts do not reach the relevant teams and external agencies in time to coordinate a response. Majority of the times inefficient effective response system leads to recording the incidents after they have occurred. In such situations, even a short delay can have serious operational and safety consequences in environments like airports, prisons etc.  

    To build an effective response mechanism, human element also plays a major role. The operators need to be trained to identify threats, analyse airspace data, and take immediate actions in emergency situations. It is important to ensure that counter UAS systems should be installed in every critical area to prevent the risk from air attacks. 

    The Way Forward

    The key question for security managers is no longer whether drones present a threat. The question is whether their organisation can detect, assess and respond to that threat in real time. Effective protection now depends on combining aerial threat detection, trained operators and clear response procedures within a single integrated security operation. 

  • From Monitoring to Decision Making: The Role of the Modern Control Room

    From Monitoring to Decision Making: The Role of the Modern Control Room

    Why Human-Centred Control Rooms Outperform Tech-Heavy Setups

    Organisations across the UK are operating in an environment where incidents are not only increasing in volume, but also in speed and complexity. In the past year alone, UK businesses experienced an estimated 8.58 million cyber-crime incidences, while 20% of businesses reported at least one cyber incident, often facing repeated attacks. At the same time, nationally significant cyber incidents are now occurring at a rate of around four per week, highlighting how frequently organisations are required to respond under pressure.   

    Most organisations already have control rooms in place, bringing together systems, screens, and teams to monitor operations and manage incidents. However, when pressure builds and multiple issues unfold at once, these environments are not always designed to support fast, clear, and coordinated decision making when it matters most. Whether managing disruptions across critical infrastructure, transport networks, or large-scale facilities, the expectation is the same: respond quickly, stay aligned, and remain in control.  

    In practice, the most effective control rooms present information clearly and support sound judgement. They also enable operators across agencies to work together and make timely decisions when it matters most. 

    Human-centric design plays a critical role in achieving this. Operators need immediate clarity on what is happening, without navigating multiple disconnected systems. Information should highlight priorities, guide attention, and support confident decision making. Every element within the control room should serve a clear operational purpose. 

    Equally important is how teams come together. Incidents rarely sit within a single function. Security, IT, and operations must align quickly to manage impact. Environments that enable shared visibility across these functions allow teams to work from the same real time picture and respond as one. This reduces delays, removes duplication, and strengthens overall coordination.

    Operational efficiency is achieved by reducing unnecessary steps between detection and action. Integrated monitoring, intuitive layouts, and clearly defined workflows allow teams to move quickly without losing control. The objective is not simply the speed, but accurate and consistent decision-making under pressure.  

    Performance under pressure is also a key consideration. Control rooms must support sustained focus during critical events. Design elements such as layout, lighting, and ergonomics directly influence how well teams can maintain attention and perform over extended periods.  

    A well-designed control room is not just a space. It is a strategic capability that reflects how an organisation prepares for and manages risk. It brings together people, processes, and technology in a way that supports better decisions in real time.  

    When designed with purpose, the control room becomes a place where complexity is managed, not amplified, and where teams are equipped to respond with clarity, confidence, and control. 

    In practice, the most effective control rooms are rarely those with the greatest quantity of technology. They are the ones that present information clearly, support sound judgement, and enable operators to work together across agencies to make timely decisions when it matters most. 

  • Building Border Resilience in an Era of Geopolitical Instability 

    Building Border Resilience in an Era of Geopolitical Instability 

    Building Border Resilience in an Era of Geopolitical Instability

    Border authorities operate in an environment where global events reshape passenger flows with little warning. A political crisis, sudden travel advisory, or regional instability can quickly lead to diverted flights, surges in arrivals, and increased pressure on border control points. 

    When that happens, the impact is first felt at the frontline. Arrival halls fill quickly, passport control queues lengthen, and officers must process travellers while working with incomplete or evolving information. In these moments, border resilience is tested by the quality of intelligence and coordination supporting frontline operations. 

    Even brief disruptions in information flow can have operational consequences. If traveller data arrives late or intelligence updates fail to reach operational teams in time, officers rely on partial information while maintaining throughput and security standards. This can result in slower processing, increased pressure on staff, and a greater risk of errors. 

    For this reason, resilience in modern border security extends far beyond physical checkpoints or individual technologies. It depends on integrating intelligence, technology, processes, and people to support informed decision-making and a coordinated operational response. 

    Situational awareness has become central to this process. Border authorities increasingly rely on systems that monitor travel patterns, flag potential risks before travellers reach the control desk, and provide officers with the information they need to make timely decisions. When these systems function well, higher risk cases can be identified earlier, allowing officers to focus on attention where it matters most. 

    This approach helps maintain controlled throughput even during periods of disruption. Passengers continue to move through the system efficiently, while security checks remain targeted and proportionate.

    Collaboration also plays a significant role in maintaining operational stability. Airlines, regional partners, intelligence agencies, and domestic law enforcement all contribute pieces of information that shape the border picture. When those insights are shared rapidly and integrated into operational systems, authorities gain a clearer understanding of emerging risks before they reach the border itself.  

    The practical benefit is straightforward. When emerging threats are visible earlier, authorities can adjust resources, strengthen screening where necessary, and manage passenger flows more effectively before disruption spreads across the border environment.  

    AI is now becoming very valuable in assisting control of border lanes, managing pedestrian and vehicular traffic queues to maximise efficiency and reduce delays, automatically detect left articles in X-ray scanner trays, over-height baggage, and dangers such as hands on conveyor belts.  

    A holistic approach to fast throughput, lane optimization, and safe but fast use of scanners to provide real time actionable intelligence to the relevant departments and personnel to react fast and proportionately. 

    The border is not limited to the checkpoints; it also consists of physical barriers, whether sea, river or fence, which must also be protected and monitored in real time, allowing for early detection and classification of threats from persons and vehicles, with drones supporting threat verification and real-time monitoring and tracking. 

    On a border of any length, these sensors can number in their thousands, making it a very complex picture for human operators to monitor and have full real time situational awareness of. Therefore control rooms and control solutions must be capable of monitoring the health status of the sensors and their activations and data sent, in real time to link and integrate sensors to give multi-factor intelligence such as, a sensor/radar detecting an object/event that might be a threat being linked to the correct and linked video feed from a camera/cameras and the launch of a drone to track and send live images of moving threats if it meets the threat response criteria. 

    The required ability of the control solution for any border is to handle the myriad of normal activities, events, detections and daily happenings in real time, and to automatically and clearly show exceptions or possible threats to the relevant personnel monitoring and offer a preprogrammed and agreed operational procedure to react and counter them.  

    Ultimately, resilience depends on how effectively intelligence, technology, processes, and people are integrated into border operations. Some organisations still build their processes around stable conditions and treat crises as exceptional events. Others are recognising that instability is becoming a constant feature of the operating landscape. 

    For these authorities, resilience must be a core design principle, balancing security, facilitation, and operational continuity. This means maintaining effective control, enabling the efficient movement of people and goods, and ensuring operations can adapt quickly when conditions change.